| Work Environment and Personal Safety Protective Measures for the Employee |
|---|
| We believe that safety and health shall be equally important to construction operations. By the implementation of the system, we ensure the quality as well as the safety and health of the construction workers by continuous improvement of occupational safety and health operation. Besides complying with occupational safety and health laws, the procedures and measures of occupational safety and health are established and promoted on a basis of discipline, safety, sanitation, health, and professionalism. |
We promise:
|
| We pay great emphasis on the safety and health of the employee, including the traffic safety of employees getting on and off duty, health examination before employment, regular health examination after employment and health promotion. We also promote an on-site service plan to create a healthy work environment and have safety and health promotion before the employee enters the factory, providing personal PPE (safety helmet, safety shoes, goggles, earplugs and earflaps, etc.), weekly educational promotion of the working SOP regularly (work aloft, power usage, hot work, confined spaces and high risks, etc.), strengthening the professional field of the employee, randomly hold courses for education and training of departments with a series of complete course specifications and implement it thoroughly.
We organized two employee-focused events in 2025, sharing practical sessions on building a supportive workplace environment and addressing common shoulder, neck, and lower back discomfort. In September 2025, the company also conducted annual employee health checkups, continuing its commitment to protecting employees’ workplace conditions and personal well-being. |
| To protect job safety of the Company’s employees in each department and the safety of the Company’s property and equipment, we established an emergency response plan intending to enhance the response ability of the employee toward emergency situations (accidents and disasters) and establish the correct procedure. By continuous training and assessment of employees, we expect they will be skillful in emergency response and accident prevention procedures with the correct knowledge in case of emergency to ensure the lives and safety of the employee and safe facility operation in the factories. |
| A complete fire fighting system was established based on the regulations of the Fire Services Act. While the fire fighting and escape equipment are checked quarterly, we also conduct emergency response drills for fire accidents every 6 months, arrange a periodical plan, and act accordingly to review and confirm the effectiveness of the system. The Company has appointed first-aid personnel to stay in the workplace in accordance with the laws and established a unit for labor safety and health management, consisting of a management specialist and staff to take charge of the labor safety and health affairs as well as to assist the safety and health promotion in each factory. |
| Meanwhile, to promote the safety and health efficiency to be in line with the international standards, the Company has received the international certificate of OHSAS 18001 Occupational Health and Safety Management Systems in 2006 and converted to ISO 45001 national certificate in April 2020. To implement the occupational safety and health policy, we consider the hazard risk through the identification of internal and external issues, risk assessment, and regulatory review. For parts that may cause significant safety and health risks along with the internal and external requirements and expectations, we set goals, targets and management programs for management and improvement. In addition, we also provide channels for employee complaints and suggestions to shape a quality safety and health culture and improve the corporate image of the Company by listening to the suggestions of the employees. Moreover, the Company continues to hire external auditors for audit certification to realize the foundation of sustainable corporate operation and development. |
| With the rise of environmental awareness, the Company puts great emphasis on environmental protection. The benefit and contribution of promoting an environmental management system is the effective control of the air and water pollution, waste, toxic substances, and noise pollution, respectively, to achieve the advantages of waste and cost reductions while effectively decreasing the risk of damage to the overall environment and fulfilling the declaration of sustainable management. In 2009, the Company also installed LEDs to save energy and reduce the carbon footprint with the goal of making a contribution to protecting the earth. |
| I. Communication between the Independent Director, Supervisor, Chief Internal Auditor and CPAs |
|---|
| The independent directors and supervisors shall hold a regular meeting with the CPAs at least once a year. The CPA shall report to the independent directors and supervisors regarding the financial status, the financial and overall operating status of the subsidiaries, and the internal audit conditions. Also, they shall have sufficient communication focusing on whether the journal entry has any significant adjustment or whether the amendment of the laws has an impact on the accounting; meeting shall be convened at any time in case of significant irregularities. |
| The Chief Internal Auditor shall hold a regular meeting, at least once a year, with the independent directors and supervisors to submit a report regarding the Company’s implementation status of the internal audit and internal control operation status; the meeting shall be convened at any time in case of significant irregularities. |
| Ⅱ. Summarized Communication between Independent Directors, Supervisors and CPAs | ||
|---|---|---|
| Date | Key Communication Points | Communication Results |
|
2024/11/07 Communication Meeting |
|
No objections were raised in this meeting |
|
2024/03/12 Communication Meeting |
|
No objections were raised in this meeting |
|
2023/03/16 Communication Meeting |
|
No objections were raised in this meeting |
2022/03/17 Communication Meeting |
|
No objections were raised in this meeting |
|
2021/11/04 Communication Meeting |
|
No objections were raised in this meeting |
|
2020/03/19 Communication Meeting |
|
No objections were raised in this meeting |
|
2019/03/14 Communication Meeting |
|
No objections were raised in this meeting |
|
2018/03/22 Communication Meeting |
|
No objections were raised in this meeting |
| Ⅲ. Summarized Communication between the Independent Director, Supervisors and Chief Internal Auditor | ||
|---|---|---|
| Date | Key Communication Points | Communication Results |
|
2024/11/07 Communication Meeting |
|
|
|
2024/03/12 Communication Meeting |
|
|
|
2023/03/16 Communication Meeting |
|
|
|
2022/03/17 Communication Meeting |
|
No objections were raised in this meeting |
|
2021/03/19 Communication Meeting |
|
No objections were raised in this meeting |
|
2020/03/19 Communication Meeting |
|
No objections were raised in this meeting |
|
2019/03/14 Communication Meeting |
|
No objections were raised in this meeting |
|
2018/05/03 Communication Meeting |
|
No objections were raised in this meeting |
|
2018/03/22 Communication Meeting |
|
No objections were raised in this meeting |
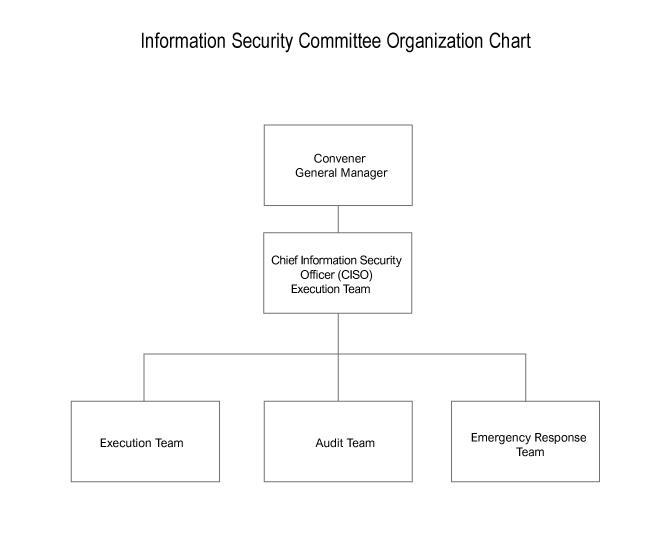
| Information Security Committee |
|---|
|
| Duties and Responsibilities of the Information Security Committee |
|
1. Responsible for promoting the implementation of information security tasks and policy planning. |
|
2. Formulate information security policies, management principles, and standards. |
|
3. Conduct information security education and training. |
|
4. Review and ensure that the ownership and control of information assets are properly managed. |
|
5. Monitor, investigate, and handle major information security incidents reported to the Information Security Committee. |
|
Information Security Risk and Incident Handling |
|
1. In the event of a major information security incident involving the company’s operational secrets that may result in losses to the company or investors, the Chief Information Security Officer (CISO) shall immediately convene an informational security meeting to decide on emergency response measures and execute them without delay. The execution results shall be reported to the next meeting of the Board of Directors, along with explanations and improvement actions. |
|
2. If a major information and communication security incident results in losses — including those affecting operations, reputation, or other aspects — an information security meeting shall be convened to investigate and handle the matter. Upon completion of the investigation, a full report including the cause of the incident, related financial losses, other losses (such as damage to reputation, etc.), handling procedures, and corrective measures shall be presented to the Board of Directors for explanation |
|
3. Once a major information security incident is confirmed by the Information Security Committee, affected customers and stakeholders shall be notified within 24 hours. |
| Information Security Disclosure |
|---|
| Year 2024 (R.O.C. Year 113) |
|
The company’s information security report has been presented to the Board of Directors. A summary of the report is as follows: The Company has established an Information Security Committee and formulated relevant management regulations. Related information has been disclosed on the Company’s official website. In terms of information security management and maintenance, the Company has established an Information Security Management Policy and corresponding procedures as the guiding principles for internal control. Internally, all company computers are equipped with certified antivirus software, and information security awareness training is conducted quarterly across all departments. Externally, professional firewalls are deployed, and the Company participates in Chunghwa Telecom’s “Cybersecurity Fleet” program for enhanced network protection. For access control, the Active Directory (AD) account management system has been implemented; for file protection, both a document management system and a data encryption system are in place. Additionally, an internet behavior management system has been introduced to strengthen external defenses. In 2024, the Company continued to strengthen its information security management, completed vulnerability scanning for critical systems, and replaced the Spam and Mail Servers to enhance email communication security. Both internal and external information security audits found no abnormalities, and no major information security incidents occurred. For the upcoming year, the Company will continue to enhance website certificate management and vulnerability scanning, promote information security awareness, and reinforce the implementation of information security management. Furthermore, the Company will strengthen its information security management systems, update management standards, and increase manpower for information security maintenance to reduce risks and ensure overall information security protection. |